Why HIPAA Makes Receipt Handling Different in Healthcare
A practical, data-backed guide to controlling costs and automating expense workflows.
For the bigger picture, see our guide to healthcare expense management for under $10/user (2026).
A proposed update to the rule would make encryption of ePHI mandatory. This means that all electronic patient information must be encrypted to prevent unauthorized access.
- Organizations must ensure that all ePHI is encrypted, regardless of the system or device it is stored on.
- Encryption methods must be regularly updated to prevent decryption by unauthorized parties.
- Organizations must also implement multi-factor authentication (MFA) for all access to ePHI systems.
- MFA requires users to provide two or more forms of verification, such as a password and a fingerprint scan, to access ePHI systems.
Additionally, the proposed rule would require organizations to report security incidents internally within 72 hours. This means that organizations must have a system in place to quickly identify and respond to security incidents.
Organizations should begin preparing for these changes now by reviewing their current security measures and implementing any necessary updates.
Keeping this simple: Incurdesk lets your team snap a photo of a receipt and fills in the details for you. It is built for small healthcare teams. Try it free.
Patient Access to Records and Substance Use Disorder Record Privacy
Covered entities must be prepared to implement these changes.
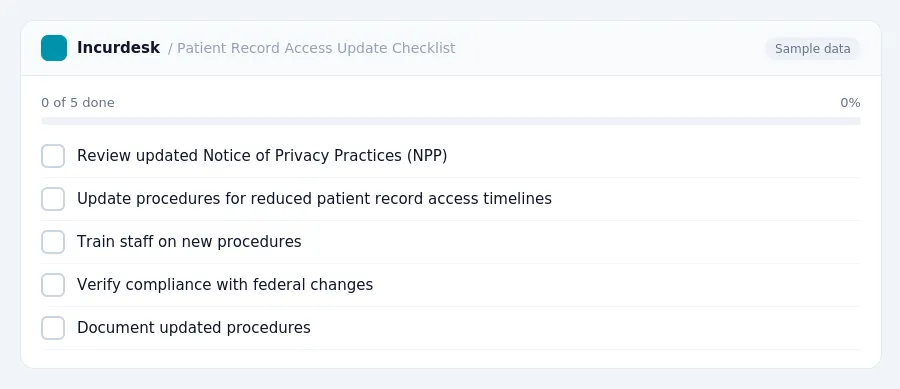
- Covered entities must update their Notice of Privacy Practices (NPP) to reflect recent federal changes, particularly those related to SUD patient records, by February 16, 2026.
Proposed changes aim to reduce patient record access timelines from 30 days to 15 days. Covered entities must review and adjust their procedures accordingly.
This includes vendors providing services such as payment processing and accounting.
For calendar year 2025 breaches affecting fewer than 500 individuals, the deadline for reporting is March 1, 2026.
For example, if a patient pays by credit card, only include the last four digits of the card number on the receipt. This minimizes the risk of a breach and reduces the need for reporting.
Limit access to these receipts to only authorized personnel who need to view the information.
Breach Notification and Reporting Requirements
Here's what you need to know:
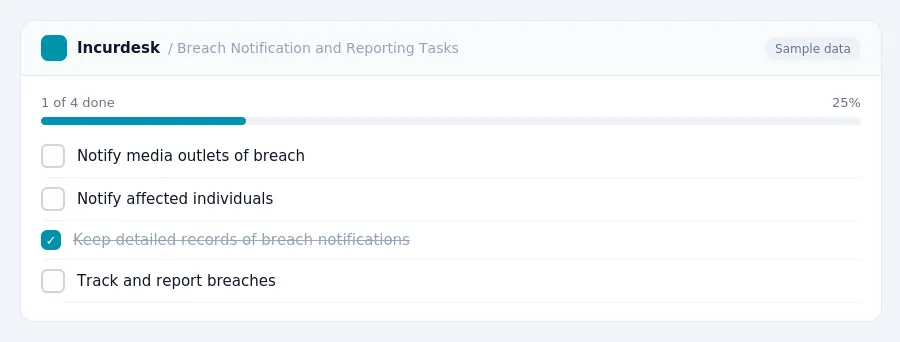
- Media outlets must be notified if 500 or more individuals in a state or jurisdiction are affected by a breach.
Individuals affected by a breach must be notified without unreasonable delay and no later than 60 calendar days after discovery.
To ensure compliance, keep detailed records of all breach notifications, including dates, times, and methods of notification. This will help you track and report any breaches that occur.
Compliance and Record Keeping for Small Healthcare Businesses
This includes updating Notice of Privacy Practices (NPPs) to reflect changes in Substance Use Disorder (SUD) record confidentiality rules.
To maintain compliance, small healthcare businesses should:
- Keep a record of all patient interactions, including receipts and billing information.
- Document all security measures in place to protect patient information, including access controls and data encryption.
- Keep a record of all breaches and report them to the relevant authorities as required.
Small healthcare businesses should also ensure that all employees understand their roles and responsibilities in maintaining patient confidentiality and complying with HIPAA regulations.
It's essential to review and update records regularly to ensure compliance and avoid penalties. The cost of non-compliance can be significant, so it's crucial to take proactive steps to maintain accurate and up-to-date records.
Tax rules, limits and rates change. Confirm current figures with the IRS or your accountant before you file.
Stop losing 4+ hours a week
30-day free trial · No credit card · Setup in 15 minutes